December 20, 2021
Software Development
Technical Debt and the art of preventative maintenance
Why build in preventative maintenance? Preventative maintenance can save a lifetime of regret and the days spent fixing vulnerabilities later.

Preventative maintenance can save a lifetime of regret. Or at the very least having to spend days fixing vulnerabilities and explaining to your customers there has been a data leak.
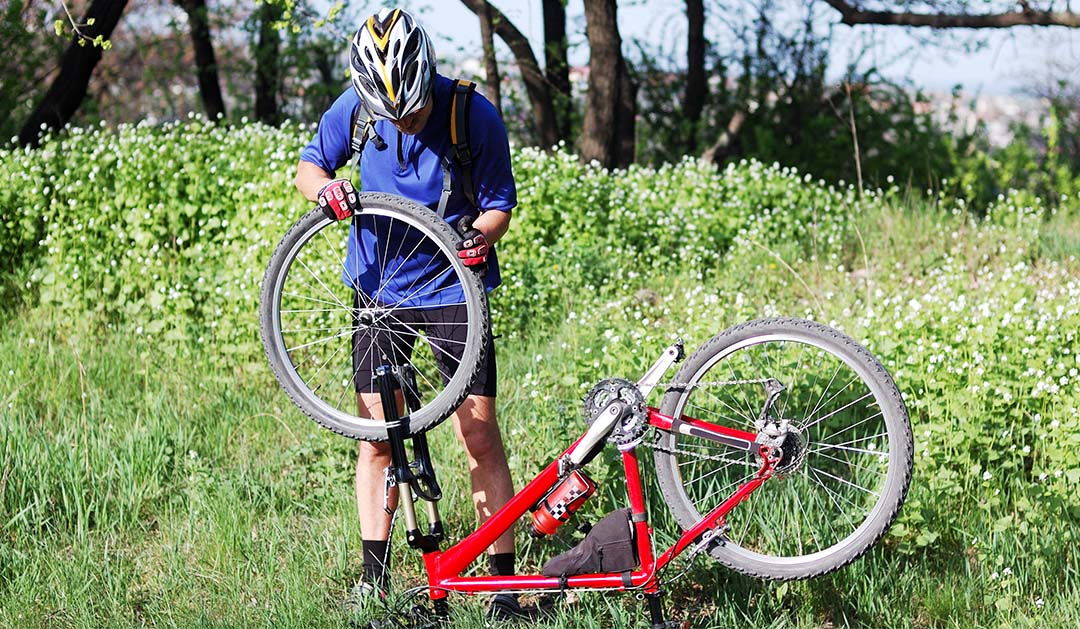
Recently, I was taking a spin around Cannock Chase on my mountain bike with a mate. Conditions were great: sunny, cool but not too cold and no rain forecast for the next 2 hours. A quick kick of the tyres and we were off to talk nonsense and enjoy the ups and downs of "Follow The Dog". 20 mins in to the ride and it started to dawn on me that my bike really shouldn't make that kind of noise when peddling and although it's fun when the back of the bike moves around on corners, it shouldn't be doing that either.
Deciding that "discretion is the better part of valour" a quick stop at the next opportunity was considered a good idea. Starting with the back tyre, yes it was almost flat and contributing to the decidedly dodgy handling. A chance brush of the pedal while pumping the tyre up raised a few eyebrows, the whole front chain ring moved with it. Quick use of the Allen key and it's all ship shape again.
Off we go for the next section. Properly inflated tyre, no more strange noises. Just in time for the rock section. Well handlebars not pointing in the right direction is considered bad form for a start. Preventative maintenance - five minutes for a spanner and a tyre pressure check and all would have been picked up and fixed before it got to be dangerous.
It's the same with web apps, mobile apps and all other software. Preventative maintenance can save a lifetime of regret.
You might be wondering why it's worth building maintenance into your product lifecycle, particularly when your project is running smoothly. The cost of the consequences are far higher than the effort of continuous maintenance and a lot more stressful.
For an example of how quickly these libraries change, between 2010 and 2020 there have been 12 major versions of Angular, six in the last two years.
When we build applications at Haywyre, we don't just look at the current requirements. We take into account the future lifecycle of the product. Planning in preventative maintenance from the day a product is released is key to reducing the long term costs and minimising the risk from vulnerabilities.
Each framework version is monitored for vulnerabilities and the fixed version brought into the project.
New releases are reviewed and scheduled for implementing in the next planned release.
Security updates and software versions are updated automatically. Performance is monitored to take into account increased traffic.
 Planning and preparation go a long way to provide peace of mind and software that doesn't age badly. In the long run, it's a best practice business decision to buy into preventative maintenance.
Contact us to find out how we can help you move your business forward.